
CISA outlines internal plan to swiftly address cyber, infrastructure threats
1 min read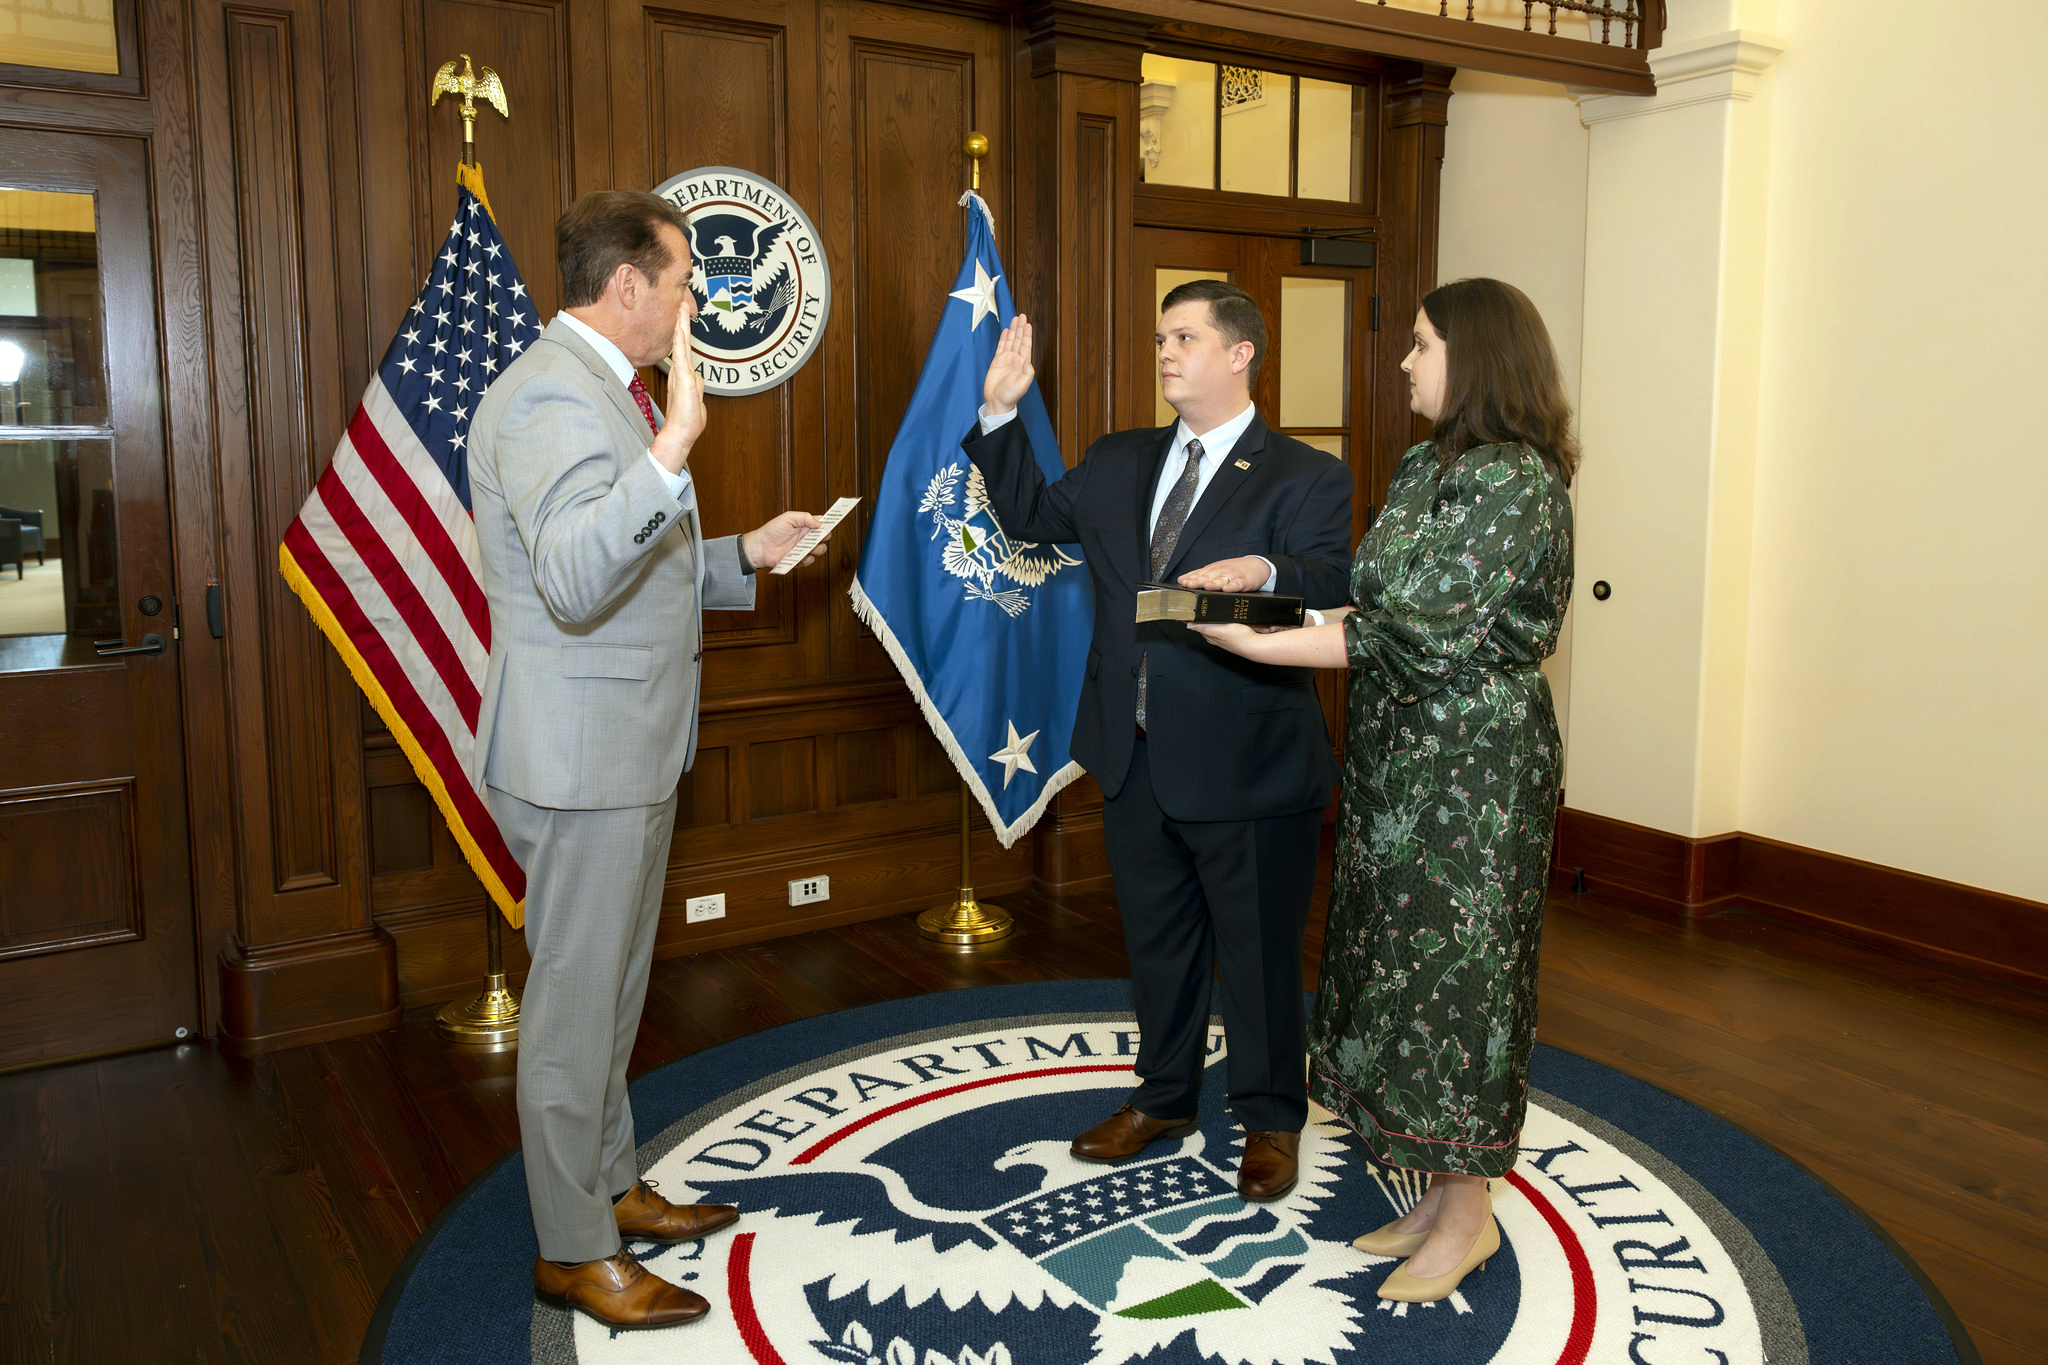
Photo caption: DHS Deputy Secretary Troy Edgar swears-in Nick Andersen, Executive Assistant Director for the Cybersecurity and Infrastructure Security Agency (CISA), at DHS Headquarters in Washington D.C., Sep. 2, 2025. (DHS photo by Mikaela McGee). Attribution: “DHS Deputy Secretary Troy Edgar Swears-In Nick Andersen” by U.S. Department of Homeland Security (DHS) via Flickr. United States Government Work. Article by David DiMolfetta. Nextgov/FCW – November 10, 2026.
The Cybersecurity and Infrastructure Security Agency circulated an internal framework last week intended to help senior officials assess major cybersecurity threats and act before they could potentially escalate into a crisis, according to an internal email viewed by Nextgov/FCW. The Nov. 5 email, which is unclassified but marked “For Official Use Only,” was sent to staff by acting Director Nick Andersen. It outlines what agency leaders need to know to assess risks and make timely decisions, aiming to help officials “cut through the noise” and distinguish useful information from what is mission-critical. […]
Click here to view the original article at www.nextgov.com
Related articles:
Trump picks Palantir cybersecurity executive to lead CISA – Cybersecurity Dive
U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog – Security Affairs
CISA updates cyber reporting form as broader incident mandate awaits approval – Nextgov/FCW

 GOOG

 IBM

 AMZN
 AAPL
 DELL
 INTC
 MSFT
 TSLA
 META
 EBAY
 NVDA
 NFLX
 HPE
 LUMN
 ORCL